Practice the incident.
Before the incident.
Scenario-driven, hands-on exercises for security teams — designed to expose gaps, strengthen response workflows and produce useful after-action evidence.
Design an exerciseRealistic environments.
Relevant missions.
Run standalone one-day sessions or build a recurring program across different threats, teams and technologies.
AI-enabled attack & defense
Investigate suspicious AI-driven activity, agent behavior and AI-assisted attack patterns in isolation.
Azure / Entra response
Identity compromise, privilege abuse, cloud telemetry, containment and recovery.
AWS attack & response
Credential misuse, exposed services, cloud logging and coordinated response.
Ransomware incident
Detect and contain an unfolding incident from initial access to business impact.
Active Directory compromise
Credential abuse, lateral movement, escalation and containment in Windows environments.
Supply chain / OSS incident
Suspicious dependencies, package behavior and correlated operational evidence.
More than a lab.
Every exercise can be structured around operational objectives, telemetry, injects and guided response — followed by a review that turns performance observations into a readiness plan.
- Scenario and mission briefing
- Hands-on investigation in a controlled environment
- SIEM telemetry and practical incident injects
- Facilitator controls and optional scoring
- After-action review with follow-up actions
See the whole environment.
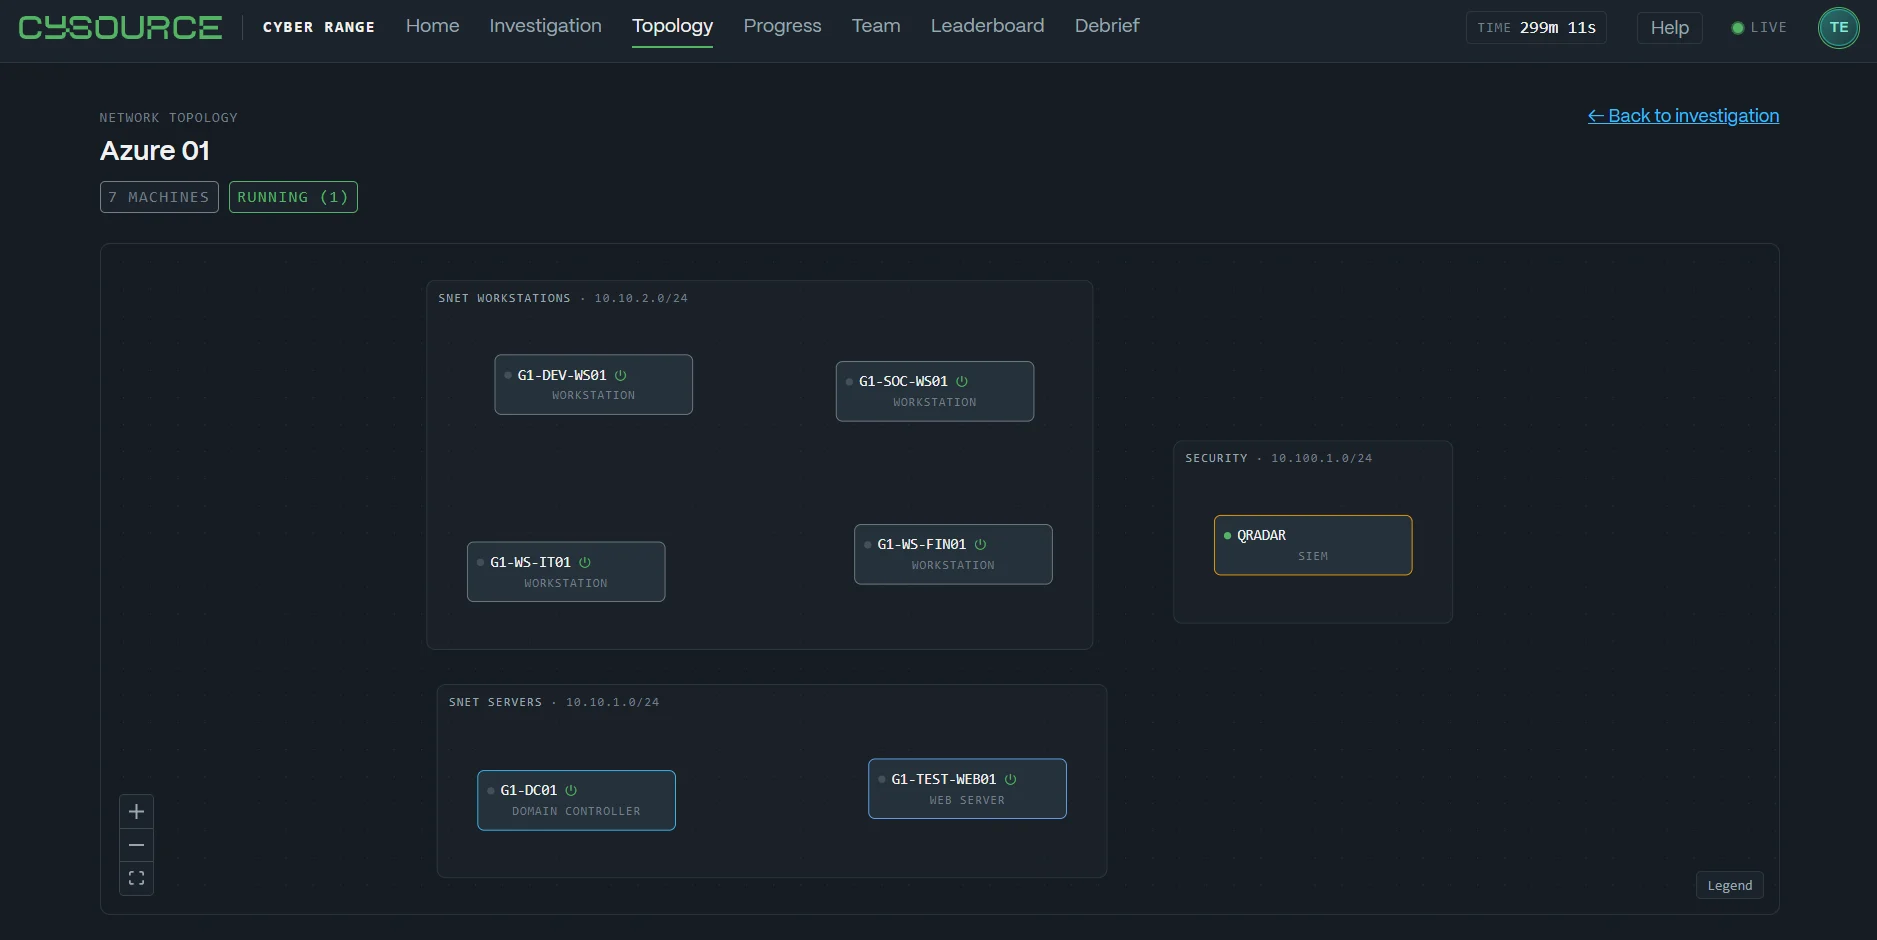
Exercises run on a live network topology, for example workstations, servers, a domain controller and SIEM, segmented by subnet, with investigation, progress, team and debrief views a click away.
Fit the exercise to the mission.
One-day scenario
A clear, contained mission with hands-on investigation and group review.
Quarterly exercise series
Rotating technologies and attack paths to reinforce readiness over time.
Client-specific range
Scenario aligned to your environment, technical controls and response procedures.