Research by the CySource research team. Originally published on cysrc.com in July 2022.
This article presents a vulnerability the CySource research team found on a website of Amsterdam Airport Schiphol: a subdomain takeover.
What is a subdomain takeover?
A subdomain takeover (STO) happens when an attacker can hijack a company’s subdomain and control the content users see when they browse to it.
Many organizations host web pages with cloud service providers. To do this, the organization creates a subdomain on its own domain and points it to the provider with a CNAME record — for example, shop.example.com pointing to a store hosted on an e-commerce platform.
The problem begins when the service behind the subdomain expires or is removed and becomes available for anyone to register. If the CNAME record is not deleted from the DNS zone, whoever claims that resource gains full control over the subdomain for as long as the record exists.
What we found on the Schiphol website
We scanned Schiphol’s subdomains and, after examining them, found this target:
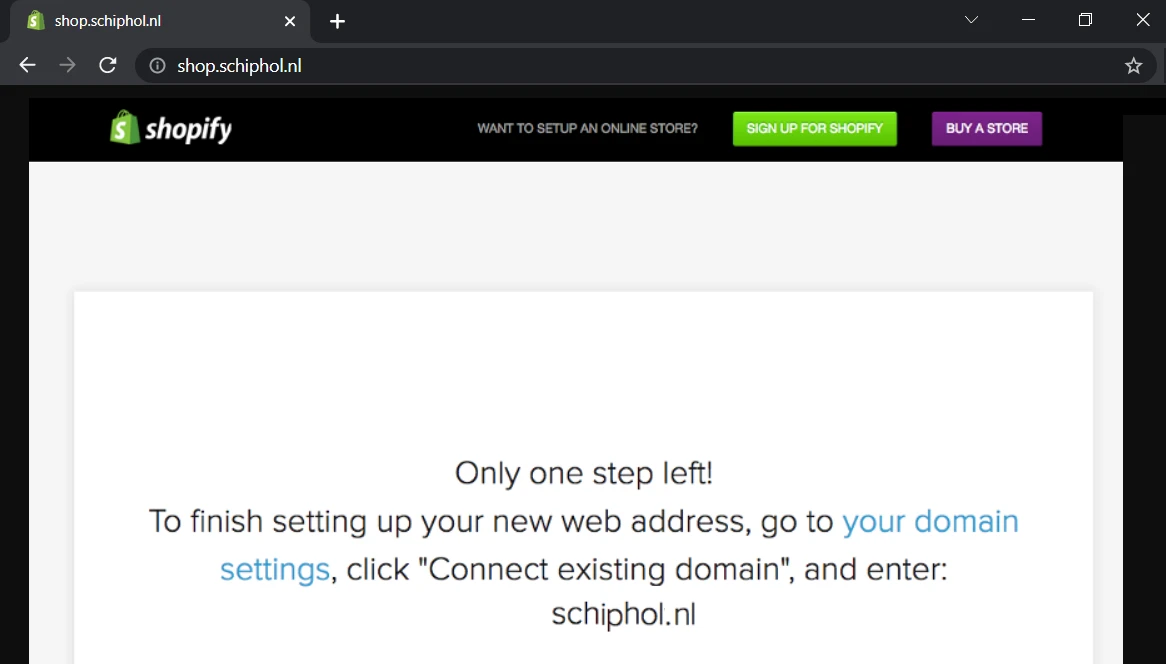
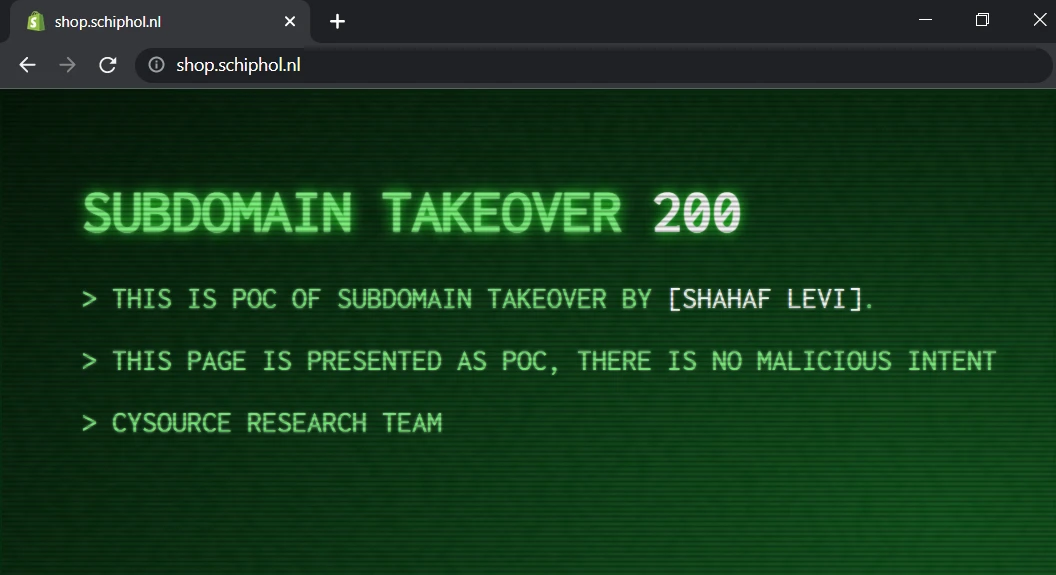
Because shop.schiphol.nl was not claimed on Shopify, we could claim it and perform the subdomain takeover. The result:
What is the impact?
With a takeover like this, an attacker controls the content of the site and can run a phishing campaign targeting users all over the world.
Here, because the site belongs to an airport and the subdomain is called “shop”, an attacker could have opened a malicious store to steal customers’ credit card and personal details. The subdomain name made the page look trustworthy from the start.
More advanced attacks are also possible, such as cross-site scripting, reading cookies set on the main domain and bypassing content security policies.